The Hidden Trap of Default AI Workflows
You copy an internal financial report, paste it into your favorite smart text generator to save some time, and hit enter. Congratulations, you might have just handed over your company's most sensitive secrets to a public database. I know the exact panic of realizing I had accidentally leaked private client data just because I did not uncheck one tiny, hidden box in my account settings. If you are using modern digital assistants at work, let me show you the invisible privacy traps you are falling into and exactly how to lock down your data before it costs you your job.
A few days later, a colleague casually asked if that specific tool used our inputs to train its public models. I completely froze. I realized I might have just handed over our most sensitive company data to the public domain without a second thought.
My heart raced as I frantically dug through their terms of service, trying to find a way to delete my chat history. That sheer panic taught me a lesson I will never forget about data security.
Right now, countless professionals are making this exact same mistake every single day. We use these smart tools to write emails, summarize meeting notes, and analyze customer feedback. We want to be faster and more productive at our jobs.
But behind the scenes, this convenience comes with a massive invisible risk. Default settings on most of these platforms are designed to collect your information, not protect it.
Every time you hit enter, you might be feeding confidential business strategies to an external server. This reality creates a heavy mental burden for anyone handling private information.
Employees live in constant fear of accidentally leaking something important and losing their jobs over a simple copy-paste error. Business owners worry about losing client trust, facing legal trouble, and watching their hard-earned reputation crumble overnight.
The stress of balancing productivity with safety is exhausting. You want to use the best technology available, but the confusing privacy policies make it feel like walking through a minefield blindfolded.
Your Quick Guide to Cloud Privacy Defense
- Turn Off Data Training: Find the hidden settings menu in your account and opt out of "Model Learning" immediately so your text isn't used to teach public systems.
- Shorten File Retention: Change your history settings to automatically delete your chats after 30 days. Never leave company PDFs sitting on external servers forever.
- Scrub Before You Paste: Always manually delete real client names, exact addresses, and specific financial numbers before pasting text into a web generator.
- Beware of Free Apps: Free tools usually pay for their server costs by harvesting and selling the exact data you paste into them.
Taking Back Control of Your Information
You do not have to abandon these amazing tools to keep your business safe. You just need to understand how to build strong fences around your private information.
Many people assume that creating an account automatically keeps their inputs private. This is a very dangerous myth that needs to be broken right now.
Most consumer-grade accounts are opted-in to data sharing by default. The platform owners want your text, numbers, and ideas to make their systems smarter.
To fix this, we need to completely rethink how we interact with third-party servers. It starts with finding the hidden toggles that most users never bother to look for.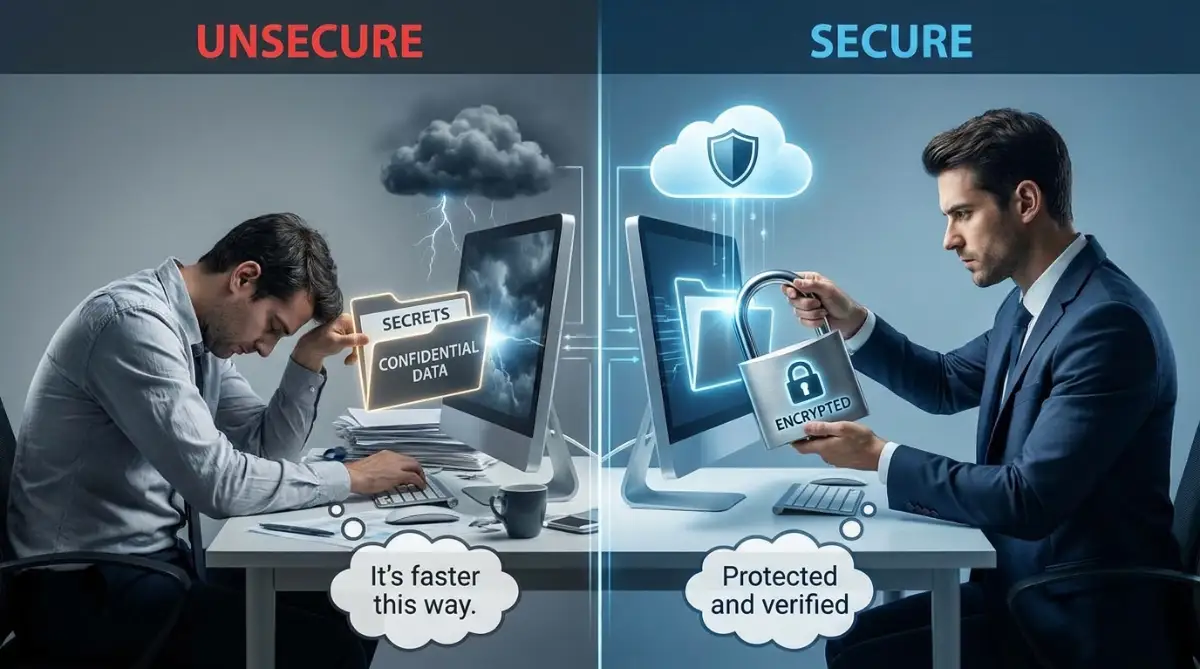
Opting Out of System Learning
The absolute most important step you can take today is finding the "Model Training" toggle. Almost every major platform has a specific setting hidden deep in the user preferences.
You need to click on your profile picture, navigate to the main settings menu, and look for a section called Data Controls or Privacy. Here, you will usually find a checkbox that allows the system to use your conversations for future learning.
Turn this off immediately. When you leave this turned on, your inputs become part of a massive global database.
Imagine typing out a list of client names and private addresses. If the system learns from that text, there is a small chance it might repeat those names to another user halfway across the world.
By flipping this single switch, you tell the server to treat your text as a temporary transaction rather than a permanent textbook. This one action eliminates the biggest risk of accidental exposure.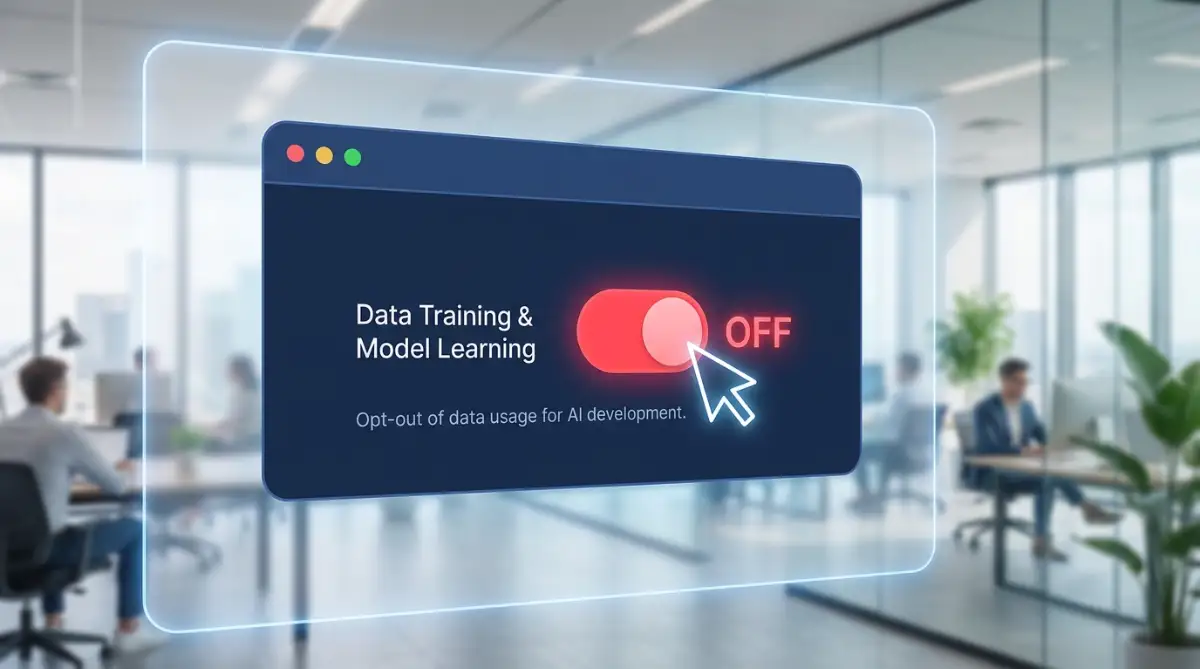
Watch This Quick Walkthrough on Finding Hidden Menus
If you are struggling to find where these toggles are buried, this short visual guide will show you exactly where to click inside the most popular dashboards.
Controlling How Long They Keep Your Files
Turning off the learning feature is a great start, but it does not mean your files are instantly deleted from their servers. We also need to manage data retention limits.
When you upload a PDF or a spreadsheet, that file sits on a cloud server somewhere. If a hacker breaches that server, your files could be compromised.
Look for a setting called Data Retention or History Management. Change the default timeline from "Keep Forever" to something much shorter, like 30 days.
Some platforms even offer an auto-delete feature that wipes your chat history the moment you close the browser window. If you are handling highly confidential HR documents or legal contracts, this instant-delete option is non-negotiable.
I once left months of private project drafts sitting in a side panel simply because I liked having them for quick reference.
My Pro Tip: I now treat my AI chat window like a public whiteboard. If I would not write the information on a whiteboard in a busy coffee shop, I do not paste it into a browser window without turning on the instant-delete feature first.
Managing Third-Party Extensions and Plugins
Connecting external apps to your smart assistant is incredibly popular right now. People love linking their email accounts or cloud storage drives directly to the platform.
This creates a brand new security nightmare. When you connect a third-party app, you are opening a bridge between your private servers and the external tool.
You need to audit every single plugin or integration attached to your account. Go to the integrations tab and review the permissions for each connected app.
Does a grammar-checking plugin really need full access to read and write all your emails? Probably not.
Revoke access for any app you do not use on a daily basis. For the apps you do keep, restrict their permissions to the absolute minimum required to function.
Understanding Enterprise vs Consumer Accounts
There is a massive difference in how platforms treat individuals versus how they treat large companies. This is where many small business owners get confused.
A free or basic subscription usually comes with zero privacy guarantees. The low cost is subsidized by your data being used for product improvement.
If you upgrade to an Enterprise or Team plan, the entire privacy agreement changes. These higher-tier plans usually guarantee that your inputs are never used for system learning.
They also offer centralized admin controls. This means a manager can turn off data sharing for every single employee in the company with one click.
A Quick Look at Account Types
If your team is using these tools for daily operations, paying for the upgraded tier is the cheapest insurance policy you will ever buy. It completely removes the burden of trusting individual employees to manage their own privacy settings.
Setting Up a Clean Environment for Testing
Sometimes you really want to test a new prompt or feature, but you do not want to risk your real business metrics. The safest way to do this is by creating a completely separate, clean environment.
Many professionals use a "dummy data" approach. Instead of pasting real sales figures, they ask the system to generate a template using fake numbers.
You can say, "Act as a financial analyst and write a report based on a hypothetical company making $50,000 a month." Once the structure is perfect, you copy the blank template into Microsoft Word and fill in your real numbers offline.
This keeps your actual revenue, client names, and strategic goals entirely off the cloud. It takes an extra five minutes, but it provides complete peace of mind.
Dealing with Browser Caches and Local Security
We often focus so much on the cloud servers that we forget about the machine sitting right in front of us. Your web browser saves a tremendous amount of temporary information.
If you are using a shared computer at a co-working space or a hotel, changing the platform settings won't help if your local browser saves the page history. Anyone sitting down after you could simply click the back button and read everything.
Always use a private browsing window when accessing these tools on a shared network. Make it a habit to clear your browser cache and cookies at the end of every work session.
Additionally, ensure your screen automatically locks when you step away from your desk. The most advanced cloud security in the world cannot protect you from a nosy person looking over your shoulder.
Creating a Culture of Mindful Usage
Technology alone cannot solve a human problem. You need to build a culture of security awareness within your own team.
Start by drafting a very simple, one-page internal policy. Do not use complicated legal jargon that nobody wants to read.
Make it a simple checklist of "Do's and Don'ts". List exactly what types of information are strictly forbidden from being pasted into external tools.
For example, public marketing copy is perfectly fine to share. However, unreleased product codes, employee health records, and client billing details should be on the absolute ban list.
Hold a quick 15-minute team meeting to explain why these rules exist. When people understand the real-world consequences of a data leak, they are much more likely to follow the guidelines.
The Real Cost of Ignoring These Steps
Let's imagine a very common scenario in a busy HR department. A manager is overwhelmed with writing performance reviews for 50 different employees.
To save time, they paste all the internal peer feedback, salary details, and personal improvement plans into a web tool. They ask the tool to generate a neat summary for each person.
If they did not adjust their privacy toggles beforehand, all of those sensitive personal details are now stored externally. If a competitor somehow gains access to that system, they could easily poach your top performers using that exact salary data.
Worse yet, if the employees find out their private reviews were uploaded to a public server, the breach of trust is permanent. The legal fines for mishandling employee records can easily bankrupt a small agency.
Taking ten minutes today to configure your data controls is a small price to pay to avoid a catastrophic business failure tomorrow.
Auditing Your Current Workflow
Do not wait until a problem happens to check your current status. Take out your laptop right now and open every single smart application you use for work.
Go through your history and look at what you have uploaded over the past month. You might be shocked at how much sensitive information is just sitting there in plain text.
Delete any old conversations that contain client names, phone numbers, or proprietary source code. Clean up your digital footprint before you change the system toggles moving forward.
If you find that an employee has been unknowingly uploading restricted files, do not panic. Use it as a coaching moment to explain the risks and help them adjust their individual account limits.
We are all learning how to navigate this new technology together. The goal is not to punish people for trying to work faster, but to guide them on how to do it safely.
What to Do If You Already Made a Mistake
If you just checked your history and realized you leaked a major project plan, take a deep breath. The first thing you need to do is hit the delete button on that specific thread.
Next, check if the platform offers a "Request Data Deletion" form in their legal or privacy section. Many companies are legally required by privacy laws to wipe your records completely if you formally ask them to.
If the exposed information involves client passwords or access keys, change those passwords immediately. Treat it exactly like you would if you lost your physical wallet on the train.
Being proactive is always better than hoping nobody noticed. Transparency with your IT department or business partners shows that you take security seriously.
Protecting your digital assets is an ongoing process, not a one-time setup. As these platforms update their interfaces and add new features, their default rules often reset quietly in the background.
Make it a monthly habit to review your security dashboards. A quick five-minute check on the first Monday of every month ensures your protective walls remain standing strong against new threats.
Going Beyond the Basics: Pro-Level Data Protection Strategies
Taking control of your basic account toggles is a great first step, but the smartest professionals do not stop there. If you want to build a truly impenetrable wall around your sensitive business information, you need to adopt a few advanced habits.
These are the exact same strategies that high-level security engineers use every day. They might sound technical at first, but I promise they are incredibly easy to apply to your daily routine.
One of my favorite methods is something I call manual data scrubbing. Before you ever copy and paste a document into a smart cloud platform, you must physically remove any identifiable markers.
Think of it like redacting a highly classified government file. If you are asking a smart tool to rewrite a client contract, you should change the real company name to something generic like "Company X".
My 3-Step Data Scrubbing Routine Before Uploading:
- Swap Names: Change "Acme Corp" to "Client A."
- Round Numbers: Change exact revenue like "$45,231" to "around $45k."
- Remove Locations: Delete specific office addresses or personal phone numbers.
- If the server gets hacked tomorrow, the stolen data is completely useless to them.
Replace real phone numbers with fake sequences, and swap out exact financial figures for rounded percentages. By doing this, you guarantee that even if a server gets hacked, the stolen information is completely useless to the attackers.
Another powerful secret involves how you actually access these platforms. Most people simply log into the standard web browser interface.
However, many major platforms offer an API connection (Application Programming Interface). When you use an API to communicate with these systems, the default privacy terms are often radically different.
Many providers automatically promise a strict zero-retention policy for data sent through their API. This means they process your request and instantly forget it, never storing it on their servers.
If your team is highly dependent on these tools, hiring a developer to build a simple custom interface using an API is a massive upgrade. It completely bypasses the risky consumer web portals.
You also need to rethink how you approach everyday tasks like how free AI generators use your private prompts and ways to stop it. Free platforms are the most dangerous because you are paying for the service with your personal information.
Instead of relying on random free tools you find on Google, invest in a single, vetted platform with a solid reputation. You can verify this by checking if the company follows strict external guidelines, such as the NIST framework for managing artificial intelligence risks.
When a provider publicly aligns with major government security frameworks, you can trust their infrastructure significantly more.
Finally, consider setting up a dedicated "clean" browser profile on your computer specifically for sensitive work. Do not mix your personal browsing with your business tasks.
Creating physical boundaries in your digital workspace makes a massive difference. Just like how cleaning your desk instantly reduces anxiety and boosts focus, organizing your digital tools gives you a much better sense of control and safety.
The Most Dangerous Copy-Paste Habits Destroying Business Security
Even with the best settings in place, human error is always the weakest link in any security chain. I have seen incredibly smart people make devastating mistakes simply because they were rushing to meet a deadline.
The most terrifying problem happening in offices right now is known as "Shadow IT". This happens when employees get frustrated with slow company software and secretly start using unapproved smart tools on their own.
Imagine a junior marketing manager who just wants to figure out how to write professional emails for immediate responses. Instead of asking for help, they paste an entire email thread containing private client complaints into an unknown, free summary generator.
The company IT department has zero visibility over this action. If that sketchy third-party tool suffers a data breach, the company will have no idea their client information is out on the dark web until it is too late.
Another massive pitfall is the false sense of security provided by browser features. So many professionals mistakenly believe that opening an "Incognito" or "Private Browsing" window protects their data from cloud servers.
Let me be very clear: Incognito mode only hides your history from the person sitting next to you. It does absolutely nothing to stop the website you are visiting from logging every single keystroke.
When you paste an internal spreadsheet into a cloud tool while using private browsing, that server still saves the spreadsheet. Relying on this myth is a dangerous habit that leads to massive exposure.
Myth vs. Reality: Incognito Mode
- The Myth: Using an Incognito or Private Browsing window hides my pasted text from the cloud servers.
- The Reality: Incognito only stops your local computer from saving your web history. The external cloud server still receives, reads, and logs every single word you type into their text box.
We also need to talk about the danger of raw data dumps. I recently spoke with a sales director who downloaded his entire Customer Relationship Management (CRM) database and uploaded it to a smart analyzer.
He wanted a quick summary of buying trends. He did not realize he had just handed over thousands of physical addresses, credit card limits, and purchase histories to an external server.
This specific action likely violated several massive international laws. If you are handling customer information, you must understand standard privacy compliance, similar to the rules outlined in the official European data protection guidelines.
Violating these laws does not just result in a warning. It can lead to millions of dollars in fines and completely destroy a brand's reputation.
However, many rogue extensions act like invisible recording devices. While you are safely typing in a secure corporate portal, a poorly coded grammar extension might be scraping the text off your screen.
This introduces risks highlighted by top cybersecurity organizations, such as the top vulnerabilities found in large language model applications. You have to secure your entire environment, not just one single platform.
It is incredibly easy to develop bad digital habits. We often zone out in front of our screens, similar to the hidden health risks of late-night scrolling you need to know. We stop paying attention to where our information is actually going.
To avoid these disasters, you have to break the automatic copy-paste reflex. Force yourself to pause for three seconds and ask, "Who actually owns this server?" before you ever press the enter key.
A Clear Roadmap to Worry-Free Smart Tool Integration
Technology is supposed to make our lives easier, not fill our days with anxiety and paranoia. You can absolutely enjoy the massive productivity benefits of these modern platforms without compromising your company secrets.
The secret lies in being intentional rather than passive. By taking just a few minutes to hunt down those hidden toggle switches, you instantly put yourself ahead of 90% of casual users.
Start by turning off all system learning features across your personal and professional accounts. Next, actively manage how long your files are allowed to sit on external servers.
If you are a manager or business owner, do not leave this up to chance. Upgrade to an enterprise-level plan that allows you to lock down the security permissions for your entire team from one central dashboard.
Educate your team on the importance of anonymizing information. Make data scrubbing a standard office procedure, just like locking the front door at the end of the day.
For an even deeper understanding of how your digital rights work across the web, I highly recommend checking out resources from digital rights advocates like the Electronic Frontier Foundation. They provide amazing insights into keeping your digital life private.
Remember that protecting your business is an ongoing habit. As platforms update and change their layouts, you need to regularly check your settings to ensure nothing has quietly reverted to public sharing.
I know this feels like a lot to manage on top of your regular workload. But taking control of your digital privacy today will give you an incredible sense of relief and confidence tomorrow. You have the power to protect your hard work, so take that first step and lock down your settings right now.
Answers to Your Biggest Smart Tech Security Questions
Can platform developers read my deleted conversations?
Usually, when you hit delete, the conversation is removed from your immediate view. However, many basic accounts retain your data on backend servers for up to 30 days for safety monitoring. Always check the specific retention policy of the tool you are using.
Does paying for a subscription automatically keep my files safe?
Not always. A standard "Plus" or "Pro" subscription for individuals often still opts you into model training by default. You usually need a specific "Team" or "Enterprise" plan to guarantee absolute data privacy.
Is it completely safe to upload PDF documents if I turn off training?
Turning off training stops the system from learning from your PDF, but the file is still stored on a cloud server. If that specific server experiences a security breach, your document could be exposed. Never upload highly sensitive legal documents unless you are using an enterprise-grade secure environment.
How do I know if an employee is using unauthorized tools?
The best way to monitor this is through your company's network firewall or IT management software. You can track which websites are consuming the most bandwidth. Open communication and providing safe, approved alternatives usually work better than strict monitoring.
What should I do if I accidentally leaked private client details?
Do not panic, but act immediately. Delete the specific chat thread, clear your session, and check if the platform offers a formal data deletion request form. Then, follow your internal company protocols for reporting a potential privacy incident to your IT department.
Disclaimer: The information provided in this article is for educational and informational purposes only. It does not constitute legal, IT, or professional cybersecurity advice. Cloud platform policies and security features change frequently. Always consult with a certified IT professional or legal counsel regarding compliance with data protection laws and specific business security requirements.